 By
A dental company operating nine practices in Northern Ireland has still not informed patients of a data breach, more than five months after being notified of the incident.
Smart Dental Care has more than 250,000 NHS and private patients across 31 practices in England, Northern Ireland, and Dublin. In Northern Ireland, they have branches in Belfast, Lisburn, Newry, Donaghadee, Ballymena, and Ballymoney.
The data breach occurred when patient and employee data was exposed after Smart Dental transferred data to a server based in the US.
The company confirmed to The Detail that there had been an “exposure of some patient and staff data.”
Subahu Shah, a board member, said they took “data security very seriously” and acted to secure the exposure as soon as they became aware of the incident in late May 2026.
Mr Shah said that employees had been notified of the breach.
But he said they had not notified patients of the data breach because it “consisted of very partial information”.
However, a cyber security researcher, who first brought the issue to The Detail’s attention, has alleged that the records in the data breach contained highly sensitive information, including patient names, dates of birth, addresses, and clinical records.
Kevin Logan, originally from Ballymena, said several of his family members, who are patients at Smart Dental Care practices here, were exposed in the data breach.
The Detail has not independently verified Mr Logan’s claims regarding the scale of the data exposed in the breach.
Some of the data was left unsecured online for almost nine months, from September 2025 until May 2026, he said.
Mr Logan contacted Smart Dental Care in late May and the database was secured six days later. In correspondence seen by The Detail, the company thanked Mr Logan for bringing the matter to their attention, and noted that they "have taken immediate action to remove access to the directory".
However, Mr Logan is concerned that, several months later, patients have still not been notified of the data exposure incident and that the company has not issued a public statement.
Mr Logan said he has informed his family members about the data breach and advised them to be careful in case they are targeted in scams.
"My cousins in the Ballymena area, they were very concerned,” he told The Detail. “I've told them just to be extra cautious.”
“When you hear stories like this in the news, people think of the organization. But they forget that every row in that database is a real person, someone’s mum or sister or dad or brother.”
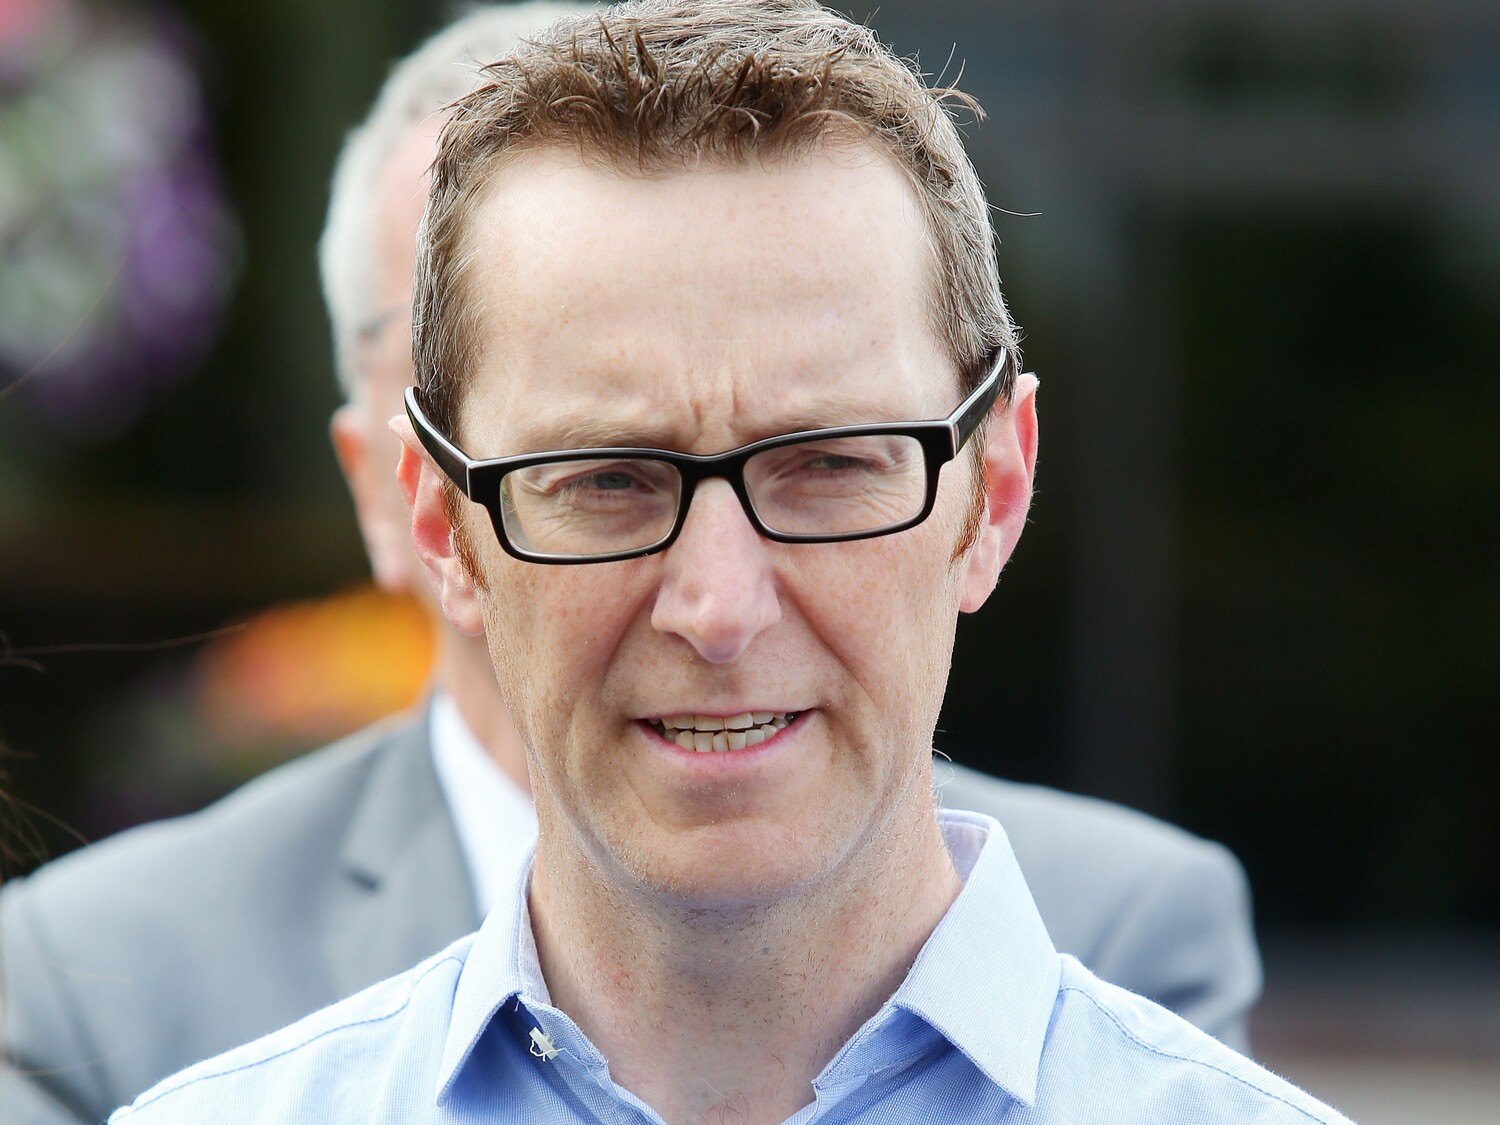
Philip McGuigan. Photo by Jonathan Porter, Press Eye
Concerns
Philip McGuigan, Sinn Fein MLA and chair of the Stormont health committee, said the reports were “deeply concerning.”
“Patients trust dental providers with highly sensitive personal and clinical information, and they are entitled to expect that information to be protected.
“Smart Dental Care need to explain what information was exposed, how long it was accessible and how many patients and staff in the north have been affected.
“The suggestion that the company has known about this incident since May, yet has not informed patients, raises serious questions. Those affected deserve a clear explanation of any risks and advice on steps they should take.”
Mariano delli Santi, a data protection expert and Legal and Policy Officer at the Open Rights Group (ORG), told The Detail that data breach rules in the UK state patients should be notified “without undue delay” if a breach poses a significant risk to them.
He said based on the cyber researcher’s claims, which he has not independently verified, “it would be very difficult for the clinic to argue that the data breach would not reach that threshold” where patients need to be notified.
“Organisations are expected to help individuals deal with potential fallout of a data breach. For instance, informing people of what has happened, what risks they might face because of the breach.”
The Information Commissioners Office (ICO), which oversees data protection in the UK, had originally closed the case in late June, stating that they had assessed the information “contained in the breach report” and had “provided data protection advice” to the company.
However, when The Detail contacted the ICO in September, we were told that they had “received new information relating to a previous personal data breach report made by Redbridge Associates Limited, trading as Smart Dental Care, and we will be assessing this latest information.”
The Detail understands that there is an ongoing live case.
The Department of Health in Northern Ireland said they are “aware of the alleged data breach”, and have contacted the company “to seek formal assurance” about the incident.
“We are asking Smart Dental to confirm whether the incident is genuine, whether the ICO has been notified, whether Northern Ireland HSC dental patients were affected, and whether appropriate mitigation measures are in place,” a spokeswoman said.
Most of the practices are based in England. Mr Logan, the researcher, raised the data breach with various NHS England bodies, including a cyber security incident in May, and with the Data Protection Compliance Team in August.
NHS England did not respond by the time of publication.
Layla Moran MP, the chair of the Westminster Health and Social Care Committee, said "a data breach of this scale concerning any area of the health service is deeply concerning.”
“Patients need to be reassured that their data is handled with care and that processes are followed to the letter when incidents occur," she added.
Smart Dental Care also has one branch in Dublin. A spokesman for Ireland’s Data Protection Commission said they were “continuing to engage with the company at this time.”